Journal Entries
Journal #1
The most appealing careers from the NICE Framework are Cybercrime Investigation,
Digital Evidence Analysis, Defensive Cybersecurity, Digital Forensics, Insider Threat Analysis,
and Threat Analysis. Cybercrime Investigations would be the most appealing out of all of them
because it seems that it would be the most intellectually stimulating and satisfying for me. It
combines the aspects of law enforcement and technology, which would require me to use critical
thinking and problem solving skills while contributing to protecting the community. Technology
Program Auditing is the least appealing to me. Although I have the skills it requires like attention
to detail and risk management, it is less dynamic and hands-on. It does not appeal to me and is
less exciting than a more technical career in the field of Cybersecurity.
Journal #2
The principles of science relate to cybersecurity because they help make sure the field is
practical and credible. Objectivity keeps personal opinions out, so cybercrime studies, for
example, are reliable. Parsimony helps simplify complex problems, like why people commit
cybercrimes, into simpler answers that we can answer and act on. Empiricism relates to using
real data, not just guesses, to understand cyberthreats and solutions. Ethical neutrality is
important when dealing with stuff like surveillance or data privacy, making sure the research
stays fair. Determinism helps explain why people do certain things online, like fall for scams or
share their passwords or personal information. That helps us come up with better prevention
methods. Finally, Skepticism makes sure we question everything, like the security tools we use,
so we don’t just take things at face value, but instead, dig deeper to figure out what really works.
All of these principles combined make sure that cybersecurity and cybersecurity research is
solid, unbiased, and helps improve the field.
Journal #3
Researchers analyze data from PrivacyRights.org to understand patterns and trends to
learn the origin of data breaches. By studying how data breaches are distributed across the
country, researchers can see where they are most common. According to the website, places
like hospitals, financial service providers, educational institutes, and businesses are targeted by
hackers the most. Organizations and the type of breach, like hacking, stolen devices, or
physical breaches, give us information on the most common methods of attack and which
locations are the most affected. To conclude, researchers can use this data to study breaches
by tracking patterns in locations, affected areas, and method of attack.
Journal #4
Maslow’s Hierarchy of Needs aligns with how I interact with technology today. At the
self-actualization level, tech supports my personal and professional growth—productivity tools
like project management apps and platforms such as LinkedIn Learning help me develop new
skills. For esteem needs, tech offers validation, like feedback on LinkedIn, where I can
showcase my expertise and gain recognition. In terms of belongingness, apps like WhatsApp,
Facebook, and Zoom help me stay connected with loved ones, while Slack fosters a sense of
community among professionals. Safety needs are addressed through devices like Ring
cameras and GPS apps, giving me peace of mind about my physical and digital security.
Technology also impacts my psychological needs, offering both benefits and drawbacks. It
provides entertainment, learning, and social connection, but overuse of platforms like TikTok can
lead to stress or dependency. Overall, technology supports my growth, connection, and safety,
but I need to manage its use to maintain well-being.
Journal #5
1: Money
The biggest motivating factor for cybercriminals is making money. There are a lot of
ways for cybercriminals to make money like identity theft, ransomware, online scams,
and stealing sensitive info.
2: Political reasons
Cybercrime for political purposes is a big deal with things like hacktivism becoming
more common. People who want to make a political statement, mess with elections, or
disrupt governmental systems often turn to cybercrime. With cyber warfare becoming
such a big part of global politics.
3: Multiple reasons
A lot of the time, cybercriminals are committing crimes for multiple reasons and it’s
common for motives to overlap.
4: Revenge
Revenge is a solid motive to cybercrime, like hacking or leaking information to get back
at someone. It might not happen as often as crimes driven by money or politics, but it is
usually because of personal issues.
5: Recognition
Some hackers want to get noticed or show off their skills. While it is not a top reason,
some people just want to make a name for themselves in the cyber world.
6: Boredom
Doing cybercrime just because you are bored is a weak reason. It assumes that
someone that commits a crime like this has a lot of time on their hands and no better
way to spend it, which actually isn’t the case for cybercriminals. It might explain random
acts of hacking.
7: Entertainment
Doing cybercrime for fun or entertainment is the least convincing reason. There is no
real purpose other than for the criminal to amuse themselves which is not a very strong
motive compared to everything else.
Journal #6
There are several ways to spot fake websites by comparing them to legitimate
ones. For instance, secure-paypal.com is a fraudulent site, as it uses a similar but
altered domain. Legitimate PayPal websites, such as paypal.com, feature secure
HTTPS encryption, valid security certificates, and official domains. Similarly,
micr0soft.com replaces the ‘o’ in Microsoft with a ‘0,’ a common tactic in phishing
scams, while the real microsoft.com has a proper domain, secure protocols, and a
professional design. Another example is applelab.co, which uses a misleading ‘.co’
domain instead of the official apple.com. Fake websites often exhibit such small
changes, lack of security, and poor design, making it easier to distinguish them from
authentic sites (Lakovics, 2024).
Journal #7
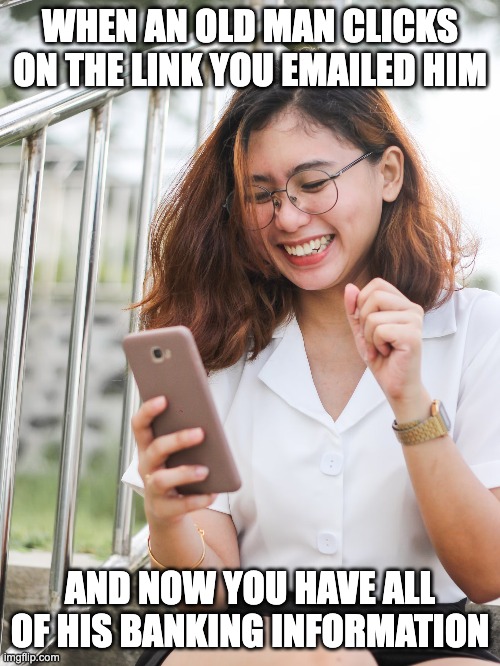
Meme 1 relates to human-centered cybersecurity because it highlights a common
cybersecurity issue called phishing attacks which exploit human vulnerabilities. Human-centered
cybersecurity focuses on educating and designing systems that help people avoid scams like
this, rather than solely relying on technological defenses. Meme 1 humorously depicts a hacker
manipulating an older individual who may be less tech-savvy into revealing sensitive
information. Effective human-centered cybersecurity strategies would involve awareness
training, better user interfaces, and fraud detection mechanisms to prevent such attacks.
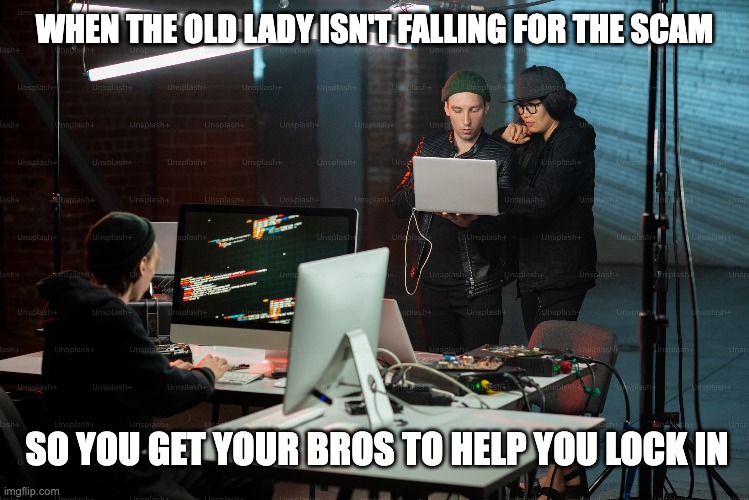
Meme 2 also relates to human-centered cybersecurity, as it humorously highlights social
engineering and coordinated cyber scams. It depicts a situation where hackers collaborate to
improve their phishing or scam tactics when an intended victim resists. This aligns with
human-centered cybersecurity because it emphasizes the human factor in cyber threats, both in
terms of attackers exploiting weaknesses and users needing awareness to defend themselves.
A human-centered approach would focus on empowering users, especially older individuals, as
implied in the meme, with better scam detection skills, multi-layered security measures, and
tools to recognize and report suspicious activity.
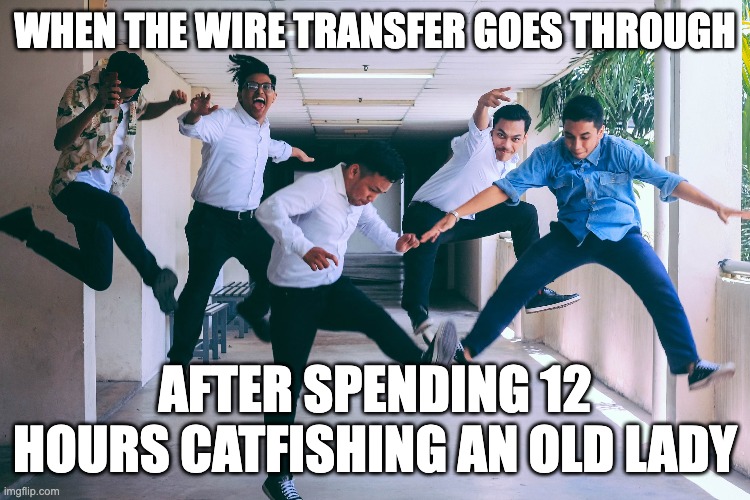
Meme 3 also connects to human-centered cybersecurity because it highlights catfishing
and financial fraud, both of which exploit human trust and emotions. Catfishing, where
scammers create fake identities to deceive victims, often leads to romance scams or social
engineering attacks that trick people into sending money. The meme humorously, but darkly
portrays a successful scam where fraudsters celebrate after convincing someone to send a wire
transfer. A human-centered cybersecurity approach would focus on educating users, especially
older adults who are often targeted about scam tactics, improving fraud detection in financial
institutions, encouraging skepticism when interacting with unknown online identities, and
developing tools that flag suspicious financial transactions.
Journal #8
The biggest thing I noticed is how the media often makes hacking seem cool. When they do
proper research, the portrayal is more realistic, and people in the industry don’t cringe when they
watch it. However, you can often tell when no research was done, or when experts weren’t
consulted. Another thing I noticed is that hacking is usually shown happening much faster in the
media than it actually does in real life. While this is probably done for plot or time constraints,
it’s unrealistic. Additionally, I’ve seen the media create things that don’t exist in reality, either for
entertainment, time-saving, or plot reasons, but, again, aren’t realistic. The media has influenced
people’s understanding of cybersecurity by simplifying and exaggerating how complex hacking
actually is. It creates unrealistic expectations which makes people think hacking and
cybersecurity is simple and easy. When experts are not consulted, it can spread misinformation
which leads to misconceptions.
Journal #9
On the Social Media Disorder Scale, I scored as “problematic usage” which is ironic
because I work in an elementary school and am constantly preaching to the kids about going
outside, having human interactions, and things of that nature. I became hooked on social media
when I was a bit older than the students I teach, but back then, society’s addiction to social
media wasn’t that intense as it is now. Yesterday, I went out to a restaurant and as I observed
people I noticed how many adults had their faces glued to their screens. A couple sitting next to
me didn’t talk, but to ask for the check and a to go box. For an hour, they sat together at a
restaurant not saying a word to each other, scrolling, texting, or tweeting. I noticed another
family across the room, who had a child in a high chair. As soon as they got settled, they pulled
out a tablet for the child. Social media/Technology addiction is a serious epidemic not only for
children, but for adults. Going through the SMD scale instilled fear in me and motivation to stop
this addiction because it is putting my goals, hobbies, and social interactions at risk. I think that
a lot of other people feel the same way, but it’s difficult to stop, especially as we are moving to a
more technology driven world. Depending on your age, I have noticed different criteria being
met, for example, withdrawal is more common in younger children, but persistence and
displacement can be seen more in adults. This is not just a me problem, or a kid problem, or an
American problem, this is a problem that is happening across the globe.
Journal #10
Social cybersecurity understanding how technology can influence our beliefs and
behavior online. The goal is to protect people in the cybersphere from misinformation and
people with malicious intent. Social cybersecurity focuses specifically on the individuals and
society as a whole while traditional cybersecurity focuses on protecting computer systems. The
example used in the text was the Russia has been using information warfare to weaken other
countries using social media and technology to create chaos and division. As technology
advances, war isn’t physical anymore; modern warfare is about influencing the mind. As we are
entering a new era of social media, it is showing us how downsides like how anyone, anywhere
can manipulate public opinion using tools like bots for example. To sum, future wars might not
just be in physical battle fields, but up in cyberspace and in the collective mind. It is up to
political and military leaders to be smarter about handling social media and information in order
to keep society safe. Social cybersecurity is key to protect us now and in the future.
Journal #11
The cybersecurity analyst profession places a strong emphasis on certifications, a
well-crafted resume, and effective networking skills, all of which are critical for personal and
professional success. Certifications are often seen as a measure of a candidate’s technical
expertise and commitment to staying current in the rapidly evolving field of cybersecurity. They
serve as tangible proof of a professional’s knowledge and ability, which builds trust and reliability
with potential employers and colleagues. A good resume highlights not only technical skills but
also soft skills such as problem-solving, communication, and teamwork, which are essential in
collaborative environments. Furthermore, networking skills are indispensable in cybersecurity,
as building connections with other professionals, attending industry events, and engaging in
online communities can open doors to job opportunities and keep analysts informed about the
latest trends and threats. From a social standpoint, these elements enable cybersecurity
analysts to demonstrate their competence, establish credibility, and foster relationships that
enhance their career prospects and professional growth.
Journal #12
Laissez-faire economic theory suggests that the government should intervene only to
protect basic rights, such as privacy. This relates to the data breach at GlassWasherParts.com,
where hackers accessed customer payment information through a third-party provider. In this
case, the government responded only after the breach, asking the company to delay informing
customers. This type of “laissez-faire cybersecurity” highlights the lack of preventative
government action, showing that without stronger rules, companies might not protect data
effectively. On the other hand, Keynesian economic theory advocates for active government
involvement to stimulate growth, such as investing in cybersecurity programs and offering tax
incentives to businesses that improve security. For instance, Virginia’s Commonwealth Cyber
Initiative (CCI) promotes research and job creation in cybersecurity. This government investment
helps reduce data breaches and strengthens the economy by fostering safer technology and a
more skilled workforce.
Cognitive theories examine how people’s thinking and beliefs influence their actions. In
the case of the GlassWasherParts.com breach, the hackers may have justified their actions by
underestimating the harm caused or believing that digital theft was less serious than physical
theft. Cognitive distortions like these help explain why individuals engage in cybercrimes,
highlighting the need for strategies to prevent breaches and hold offenders accountable.
Neutralization theory suggests that criminals justify their actions by suppressing their morals
through techniques like denial of injury or responsibility. The hackers in this case might have
believed no one was harmed, blamed the company’s poor security, or justified their actions for
personal gain. These justifications allow offenders to commit crimes without feeling fully
immoral.
Journal #13
Bug bounty programs play a crucial role in cybersecurity by allowing ethical hackers to
identify vulnerabilities within company systems. These programs, supported by platforms like
HackerOne and Bugcrowd, reward freelance security researchers for their work. However, many
companies hesitate to accept vulnerability reports from outside researchers due to the lack of
vulnerability disclosure policies (VDPs), which can protect researchers from legal risks. A recent
study by HackerOne revealed that 93% of companies in the Forbes Global 2000 lack VDPs,
discouraging researchers from reporting vulnerabilities. This trend is starting to shift, with
organizations like the US Department of Homeland Security recommending the adoption of
VDPs. Along with the rise of VDPs, more companies are adopting bug bounty programs. These
programs help businesses find hidden vulnerabilities while accessing top-tier freelance talent.
Despite their growth, research on the effectiveness of these programs is limited. One study found
that hackers are not significantly price-sensitive, meaning smaller companies can benefit from
these programs too. However, industries such as finance and healthcare receive fewer reports,
and older programs may see a decline in the number of submissions over time. Expanding a
program’s scope can help address this issue. The study also found that public programs tend to
engage more hackers but may lead to a higher number of invalid reports. In contrast, private
programs are more selective and efficient. On average, running a bug bounty program costs
about $85,000 annually, which is less than hiring two in-house engineers. Data from HackerOne
and the Privacy Rights Clearinghouse was used to analyze over 50,000 valid vulnerability reports
and 8,769 data breaches, providing insights into the impact of bug bounty programs on
cybersecurity.
Journal #14
I believe that the 5 most serious illegal activities that people commit on the Internet are
sharing personal information of others, bullying and trolling, using someone else’s internet
connection, collecting data about children, and conducting illegal searches. Sharing someone’s
passwords, addresses, or private photos without their consent is a serious invasion of privacy
and can put individuals at risk of identity theft, stalking, or emotional distress. Bullying and
trolling online are also major issues, as they can lead to severe emotional and psychological
harm for the victims, sometimes with tragic consequences. Using someone else’s internet
connection without their permission is not only unethical, but it is theft, and can expose all
involved to security risks and legal consequences. Collecting personal information about
children is especially dangerous because children are vulnerable and unable to fully understand
or consent to what is happening. This kind of exploitation can lead to long-term emotional and
physical harm. Finally, illegal searches on the Internet, such as looking up how to commit crimes
or accessing illegal content, show an intent to break them and can have serious consequences
for both the individual and society. These activities emphasize how important it is to use the
Internet responsibly and respect the rights and safety of others.
Journal #15
Digital forensics are closely tied to social sciences like psychology, sociology, criminology, and anthropology because it involves understanding human behavior and communication through technology. Investigators not only analyze technical evidence but also interpret the context behind actions. Language analysis, which includes tone and writing patters, plays a huge role in identifying suspects. Sociological factors influence digital spaces, helping investigators understand internal workplace cultures or group behaviors. Ethical considerations are essential when handling sensitive information and making responsible decisions. Also having to be able to present findings in court. Just like social sciences, digital forensics requires a host of fields and skills to be able to adequately get the job done.